PRIMARY CATEGORY → CHECKLISTS • WINDOWS PRIVESC
Mindmap

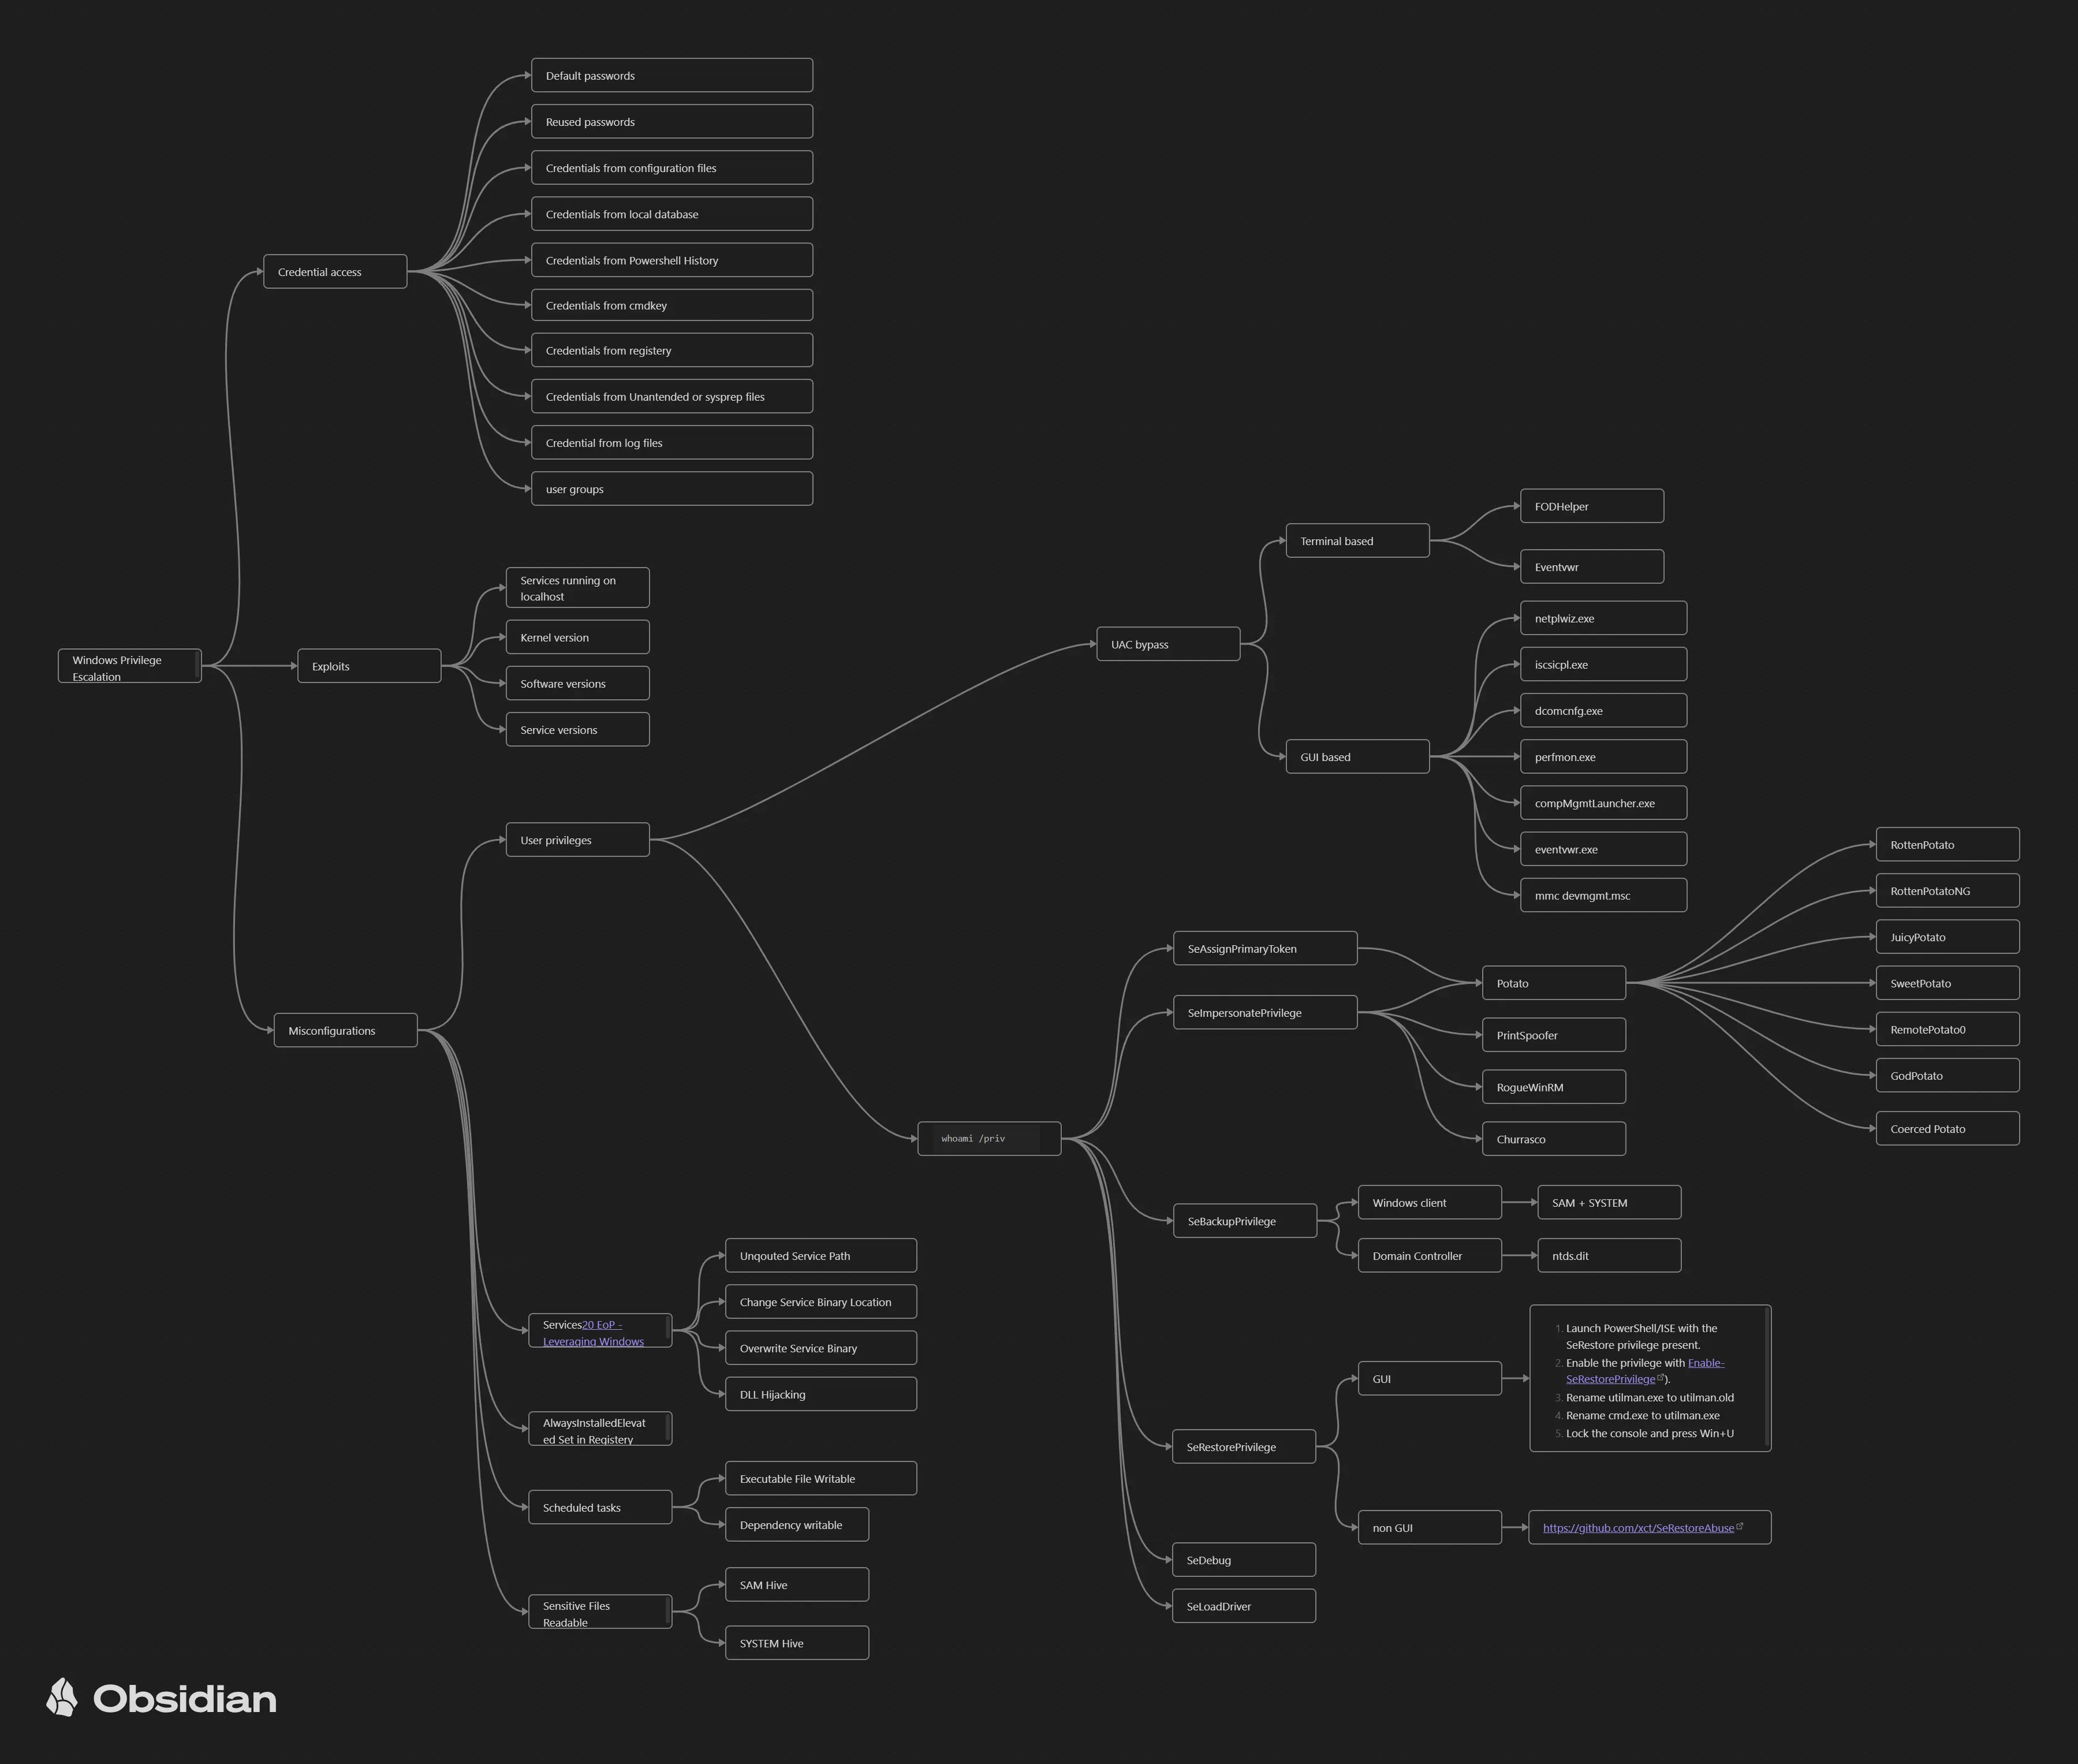
Zoom in
Non-Privileged
e.g. Network Interfaces, ARP Table, Routing Table…
-
Is the current system a domain-joined machine?
e.g. HTTP ↔ 8000 TCP Port ( 127.0.0.1:8080 )
See the point below
- Any HTTP Web Application or MSSQL Instance → Privesc to LOCAL SERVICE or NETWORK SERVICE → SeImpersonate and SeAssignPrimaryToken → LOCAL SYSTEM
e.g. A Webapp with an Upload Feature → Uploaded files not accesible externally ( e.g.
C:\Windows\Tasks\Uploads) → Current user with WRITE Privileges over the Uploads directory → Junction ( Windows Symlink ) creation pointing to the webroot → Uploaded resources accesible externally
See Media from HTB
- SeImpersonate and SeAssignPrimaryToken Privileges
From LOCAL SERVICE or NETWORK SERVICE to LOCAL SYSTEM
RoguePotato ↔ RottenPotato ↔ JuicyPotato ↔ PrintSpoofer
- Other Sensitive Windows Privileges related to the Current Access Token
e.g. seDebug, seBackup, seLoadDriver, seTcb and so on
-
Local and Domain Privileged Groups to which the Current User belongs
e.g. A local user account named Alex which belongs to Backup Operators
e.g. MRemoteNG
Sherlock ↔ Windows Exploit Suggester
Netexec ↔ Impacket’s REG.py ↔ Get-GPPAutologon
-
Directory Content Checking → C: | Program Files | Program Files (x86) | Users
-
Leaked Credentials on Local Users or Computer Description
-
Look for Powershell Credential Objects
e.g. Resources containing juicy strings such as “pass|password|passwd” and so on
See also Other Interesting Files and Unattended Installation Files
-
Credential Extraction from Browsers ( Chrome, Firefox… )
e.g. Cookies, Saved Logins…
-
Credentials stored in Windows Vault and Credential Manager
See DPAPI Abuse
- Look for system directories for which the current user has WRITE Permissions
-
Coercion through a Shortcut File Upload if the current user has WRITE permissions over interesting and busy local folders or shares
-
UAC Bypasses if needed
-
For any Microsoft Exchange Server deployed, see Sensitive Information Extraction from Microsoft Exchange Inbox
-
Check for ADS in files
-
List existing Scheduled Tasks
-
Existing Named Pipes with wrong DACLs (e.g. Everyone → Write Permissions )
-
If we land on a CITRIX Windows Restricted Environment, see CITRIX Breakout
Pillaging
Memory ( LSASS ) ↔ DPAPI Secrets ↔ Windows Secrets ( e.g. SAM, LSA… ) ↔ Config. Files
e.g. NTDS | SAM | SYSTEM | SECURITY
Impacket’s Secretsdump.py ↔ Mimikatz ↔ Netexec
More NT Hashes and even plain credentials
- DPAPI Dump → Credentials for all system users stored in Windows Vault and Credential Manager
See DPAPI Abuse
Remote DPAPI Secrets Extraction using DonPAPI
Impacket’s Secretsdump.py + ( Hashcat + John )
- Look for Sensitive Credentials again in the entire system
As we have access to the entire system ( Privileged Access )
e.g. Files with Sensitive Information, Unattended Installation Files, All PS History Files…
-
All Domain User Accounts’ Descriptions → Look for Plain Credentials
-
SMB Shares Content
Look for Plain Credentials again in the existing resources
- Check for installed Software → Look for credentials
e.g. MRemoteNG, Teamviewer and so on
Some of them automated with Lazagne or DONPAPI, but simply search for
<SOFTWARE> local creds extraction/decryption
- Check any Service running on the target → Look for credentials
XAMPP → Web Server →
C:\xampp\htdocs\wordpress\wp-config.php, MSSQL → DB Connection to look for interesting information within DBs
- If the victim has a Wireless Netword Card, see WiFi Credential Extraction
Automated with Lazagne
Credentials for all system users